FaceStealer turns a familiar face into a fake meeting. The dangerous step is the repair
The FBI warns that stolen webcam recordings and hijacked accounts help persuade targets to install malware.
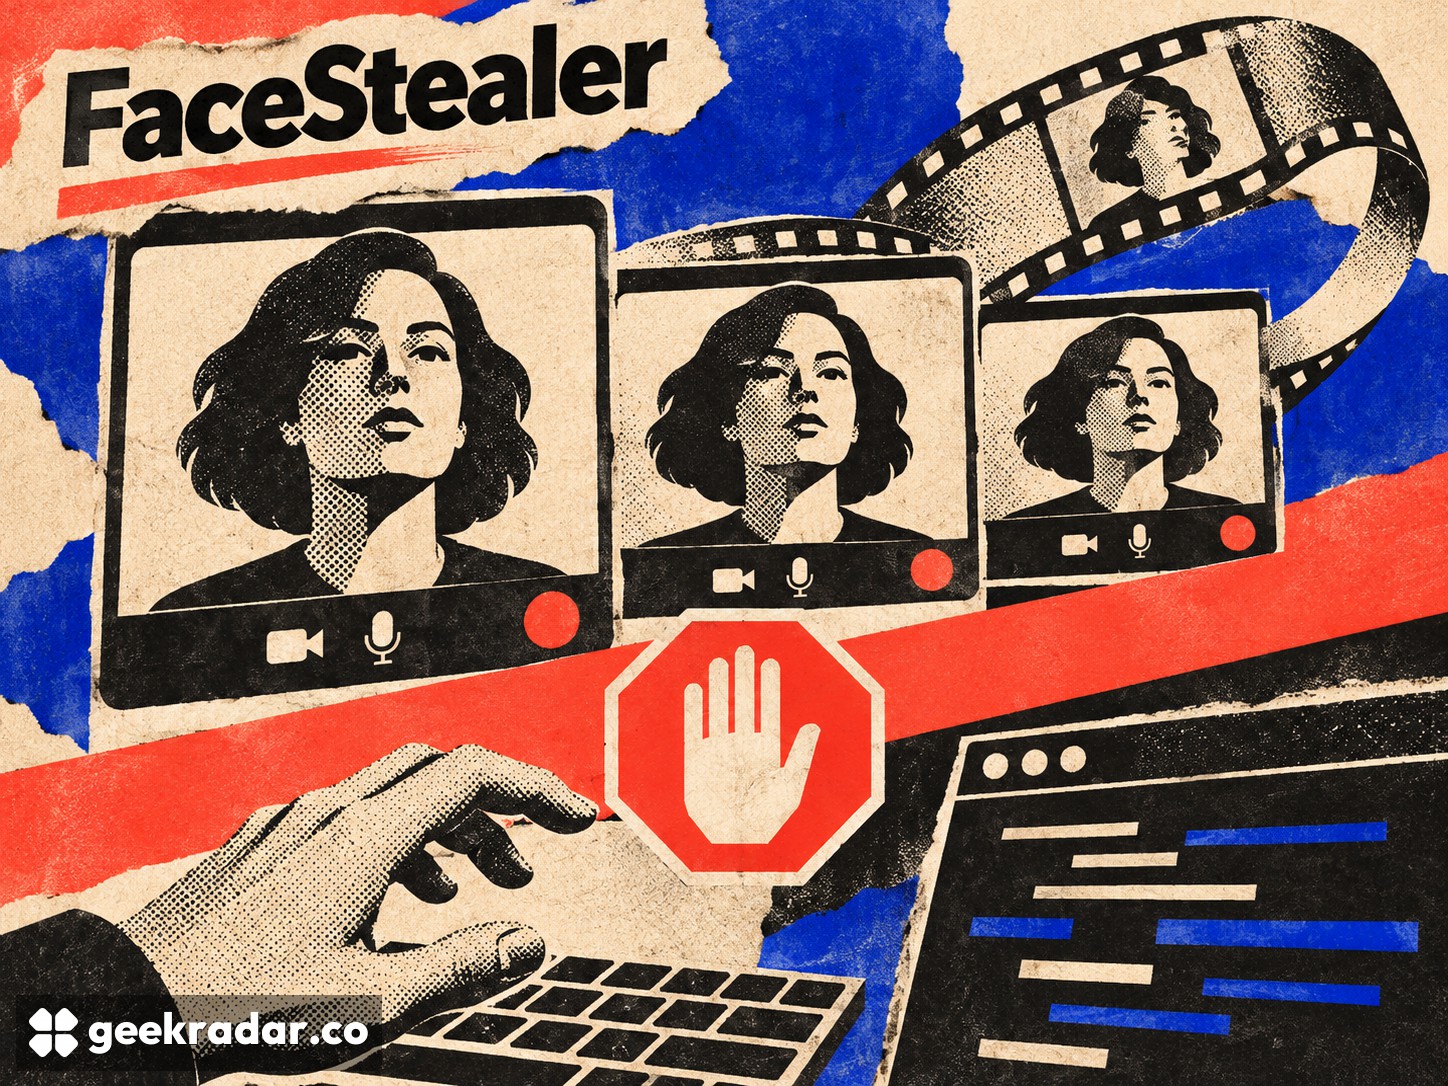
A familiar face in a video call is not enough to establish who is controlling the meeting. In a November 12 warning, the FBI describes FaceStealer, a North Korean campaign that uses hijacked accounts and recordings of previous victims to persuade new targets to install malware disguised as a technical fix.
The bureau says the campaign has stolen more than $400 million in cryptocurrency over 18 months and that it has seized over 900 victim webcam recordings. Those are FBI figures. The immediate lesson extends beyond cryptocurrency: an invitation from a real account, followed by the apparent presence of somebody you know, can still lead into an attacker-controlled environment.
The meeting borrows trust before asking for code
The chain begins with an account that has already been compromised. Attackers can read its conversations, contact people who know the owner and suggest a plausible meeting. A scheduling invitation helps make the exchange look ordinary. The actual meeting link then leads to an imitation of a familiar service.
Inside that imitation, prerecorded footage supplies recognizable participants. The target is told that audio or another component is broken and is guided toward an update, script or command that supposedly repairs it. The crucial boundary is crossed when a social interaction becomes permission to run software.
This is why the scheme is more than a convincing picture. Its strength comes from several signals reinforcing each other: a known account, relevant conversation history, a scheduled appointment and a familiar face. Each can be genuine in origin while the overall interaction is fraudulent.
These steps reflect the FBI's recommendations. They target the behavior the attacker needs, instead of asking a participant to become an expert at spotting manipulated faces under time pressure.
Stolen recordings remain central
The advisory also describes growing use of generated video, particularly to impersonate prominent people. But it explicitly says the scheme still overwhelmingly relies on recordings stolen from genuine victims. Calling every instance a deepfake attack would obscure that distinction.
A recording can look convincing precisely because the original person was real. The question is whether the current interaction is authentic, not whether every visible pixel was synthesized. Searching for odd hands or unnatural expressions therefore cannot be the main defense.
Arctic Wolf's November 12 investigation, cited by the FBI, describes related lures expanding into shared documents, media-player prompts and other professional workflows. Its researchers emphasize that the packaging changes while the essential request remains similar: trust the interaction, accept a manufactured problem, run the proposed fix. Their targeting counts are not interchangeable with the FBI's count of seized recordings or confirmed financial losses.
A developer's account can become somebody else's incident
The FBI specifically warns open-source maintainers as well as the cryptocurrency industry. Access to a maintainer's workstation or repository account can create an opportunity to alter dependencies or software distributed to many downstream users. The value of the compromised account is therefore not limited to money stored on that machine.
That is a different exposure from accidentally publishing a credential, the subject of our recent GitHub secret-scanning coverage. Both concern access that can outlive the moment it is lost. Detecting a leaked secret does not make a stolen developer session harmless, and a familiar meeting interface does not authorize the commands it presents.
If somebody has already followed a suspicious repair prompt, the advisory calls for securing affected accounts and notifying contacts and employers. Merely leaving the call does not establish that installed malware or stolen sessions have disappeared. An organization should treat the episode as a potential compromise and involve its security team.
The most useful habit is also the simplest to explain to colleagues: a meeting should not require a stranger, or an apparent friend, to turn you into the installer of its repair tool. When conversation becomes a request to execute code, stop the meeting before continuing the instructions.