Equinor says production is running normally as its cyberattack continues
Employees reported trouble using office services. Equinor’s November 19 update gives a clearer picture of output and data integrity, but no date for restoring affected systems.
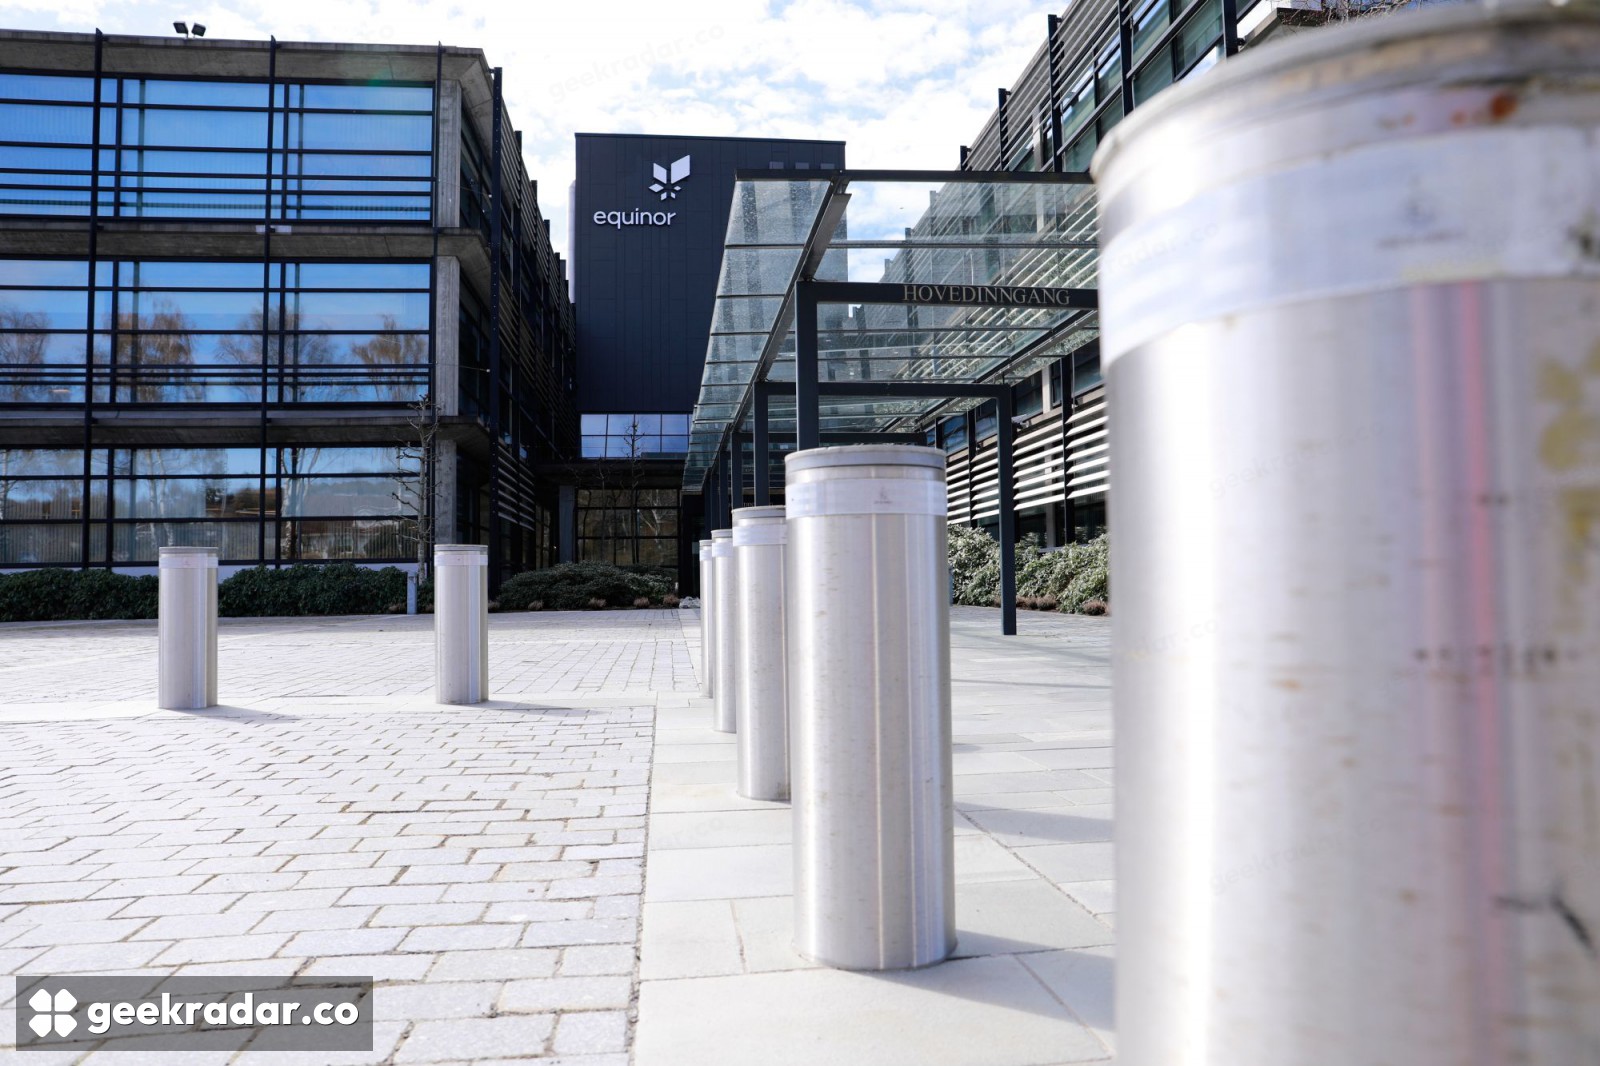
Equinor was still trying to stop a cyberattack on Thursday, two days after it disclosed the incident. The Norwegian energy company said production was running normally and investigators had found no indication that anyone had stolen or altered data. It could give customers an answer about oil and gas output. It could give employees no timetable for restoring the affected IT systems.
The disruption employees could see
Equinor’s first public notice, at 18:55 CET on November 17, identified an attack on some of its IT systems. The practical effects emerged in reporting from Norway. A company spokesperson told the Norwegian news agency NTB that employees could have trouble accessing corporate applications and services. A person at Equinor separately told Reuters that internal email was down. That was an account from Tuesday. Equinor’s Thursday bulletin gave no fresh status for email.
People can lose access to a service even while the records behind it remain intact. An employee unable to open a mailbox can report an outage straight away. Establishing whether someone read a message or changed a record takes a different kind of evidence. That distinction matters here because Equinor’s November 19 update addressed both theft and alteration while saying the work to restore confidence in the affected systems was continuing.
Why customers are watching production
Norway was the European Union’s largest external supplier of natural gas in gaseous form in the second quarter of 2026, according to Eurostat’s energy trade report. That gives European customers a reason to follow a Norwegian company’s IT incident. It also makes accuracy about its scope particularly important. The company reported no loss of production. It did not identify a platform, pipeline or industrial controller as having been compromised.
In other industrial incidents, evidence of changed equipment settings has connected remote access to a physical effect. Here the publicly reported symptom was difficulty using office services. Equinor said the attack did not appear to be aimed specifically at the company. It has not publicly identified who was responsible.
For customers waiting on deliveries, continued production was the most useful line in Thursday’s statement. For someone at Equinor waiting to trust a business application again, the consequential line came earlier in the same paragraph: the company still could not say how long recovery would take.