GitHub’s WFX attacks can leave clean files behind and stolen credentials elsewhere
New research links some affected accounts to GhostAction and shows why recovery must include runners and cloud access.
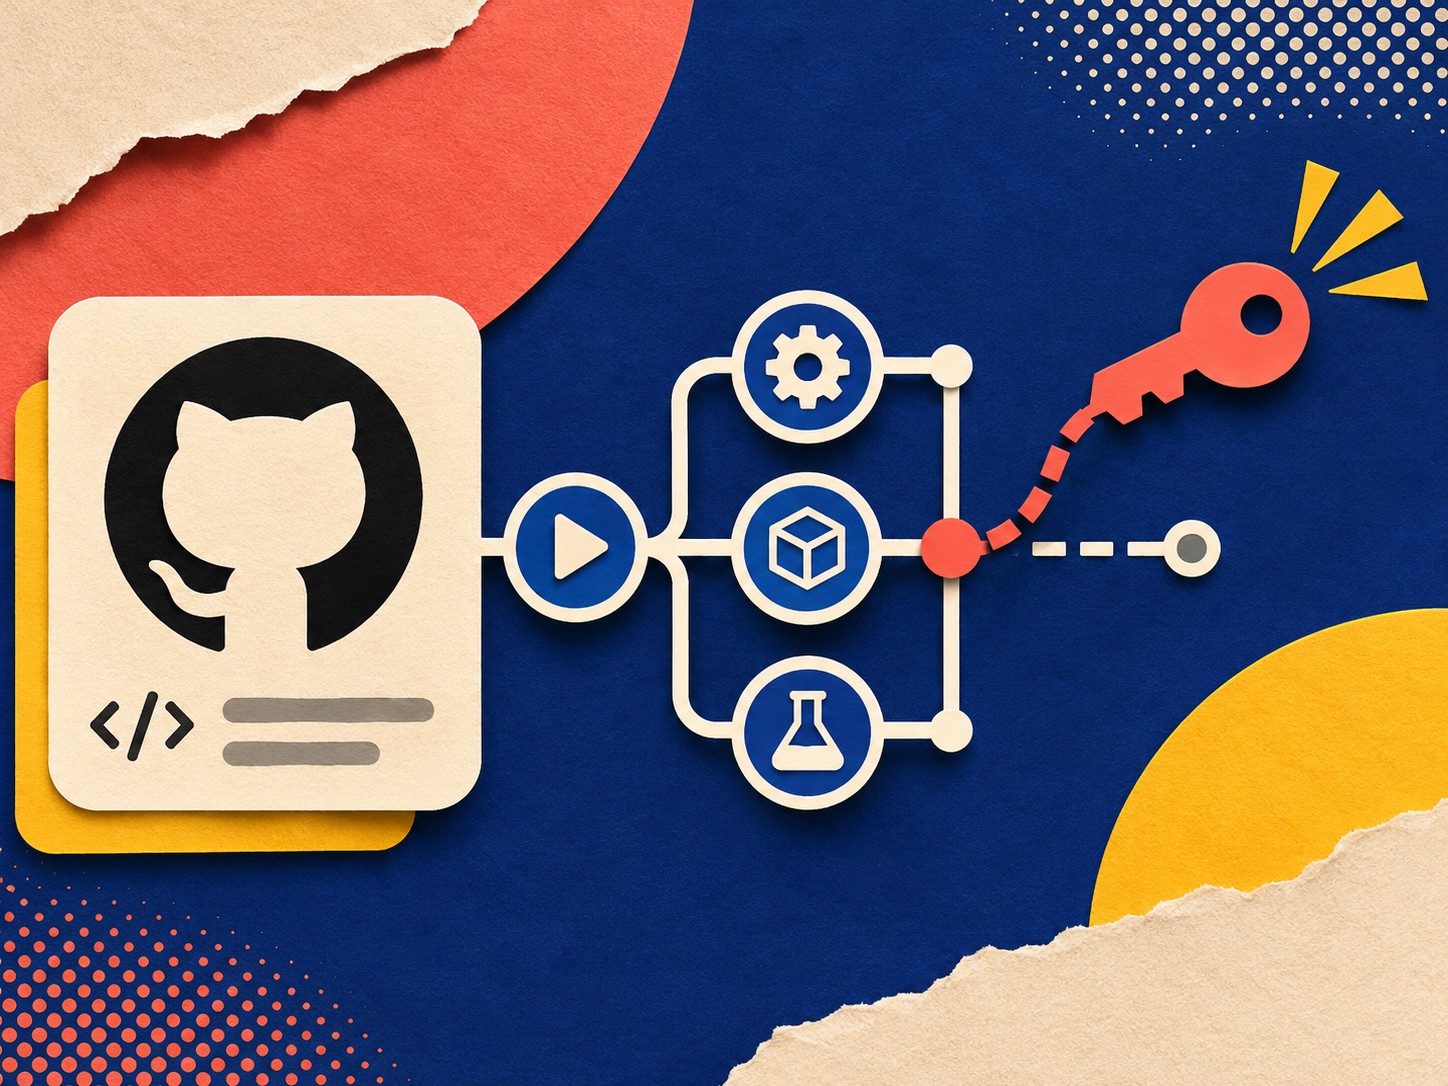
The WFX attack campaign can leave a repository looking normal after using its automation to steal credentials. That cleanup is the important warning in Ossprey’s November 12 investigation: examining only the files currently visible on the main branch can miss a malicious workflow that has already run and been removed.
The researchers traced thousands of probes across GitHub and investigated links with an earlier campaign called GhostAction. Their evidence supports a large credential-abuse operation, with some overlap between affected accounts. It does not establish that every probed repository lost secrets, or that every account was compromised through the same initial route.
A harmless-looking change can test a powerful credential
Ossprey describes small documentation pull requests used to test whether an acquired credential could write to a repository. Subsequent activity could alter an existing GitHub Actions workflow, add a helper script or create a temporary workflow. The target was the automation environment: repository secrets, workflow tokens, cloud access and credentials reachable from the runner.
This explains why a documentation-only change deserves context. Its content may be innocuous while the account making it is being used to measure access. A pull request is an observation, not proof of a successful theft; unexpected workflow changes and execution history supply the more consequential evidence.
The attacker then restored files and deleted runs or logs in some cases. A missing run number may be a clue, but it is not a diagnosis by itself. Teams need to correlate commits, account activity, workflow changes and cloud logs rather than treat a single gap as conclusive.
The GhostAction overlap has limits
Among 130 GhostAction-affected accounts still searchable in Ossprey’s sample, 33 also authored WFX probes. Another ten had repositories probed by other accounts. Those are two different forms of overlap: owning a repository someone targeted is not the same as having one’s own account used to target others.
The examined older payloads searched for developer and cloud credentials, including GitHub CLI tokens. That offers a plausible connection to later account misuse. Ossprey explicitly cannot reconstruct every initial compromise from public history, so the overlap should remain evidence of a connection rather than a complete attribution claim.
Recovery extends beyond GitHub
GitHub’s security guidance recommends minimal token permissions, review of secret use and rotation of exposed credentials. In this incident, that means identifying which services a workflow could reach and revoking or replacing their credentials at the issuer. Changing a repository file cannot revoke a cloud token or an API key issued by another service.
Cloud access through OpenID Connect also needs review. Short-lived credentials reduce the lifetime of a stolen token, but an overly permissive trust relationship can let an unauthorized workflow obtain another one. The relevant boundary includes the repository, branch or environment allowed to assume a role, not just whether a long-lived key was stored in GitHub.
Self-hosted runners deserve separate investigation because they are persistent machines. If attacker-controlled code ran there, rebuilding from a known-good state may be necessary after preserving incident evidence. Restoring the repository alone leaves the machine outside the recovery plan.
The campaign’s most useful lesson is procedural: validate restored access, not merely restored files. A repository can regain its familiar appearance long before the services it can reach are safe to trust again.