AWS secret replicas cross account boundaries, but stay inside one region
A receiving account gains its own key and policies. Asynchronous updates and a one-replica limit shape what this can do for recovery.
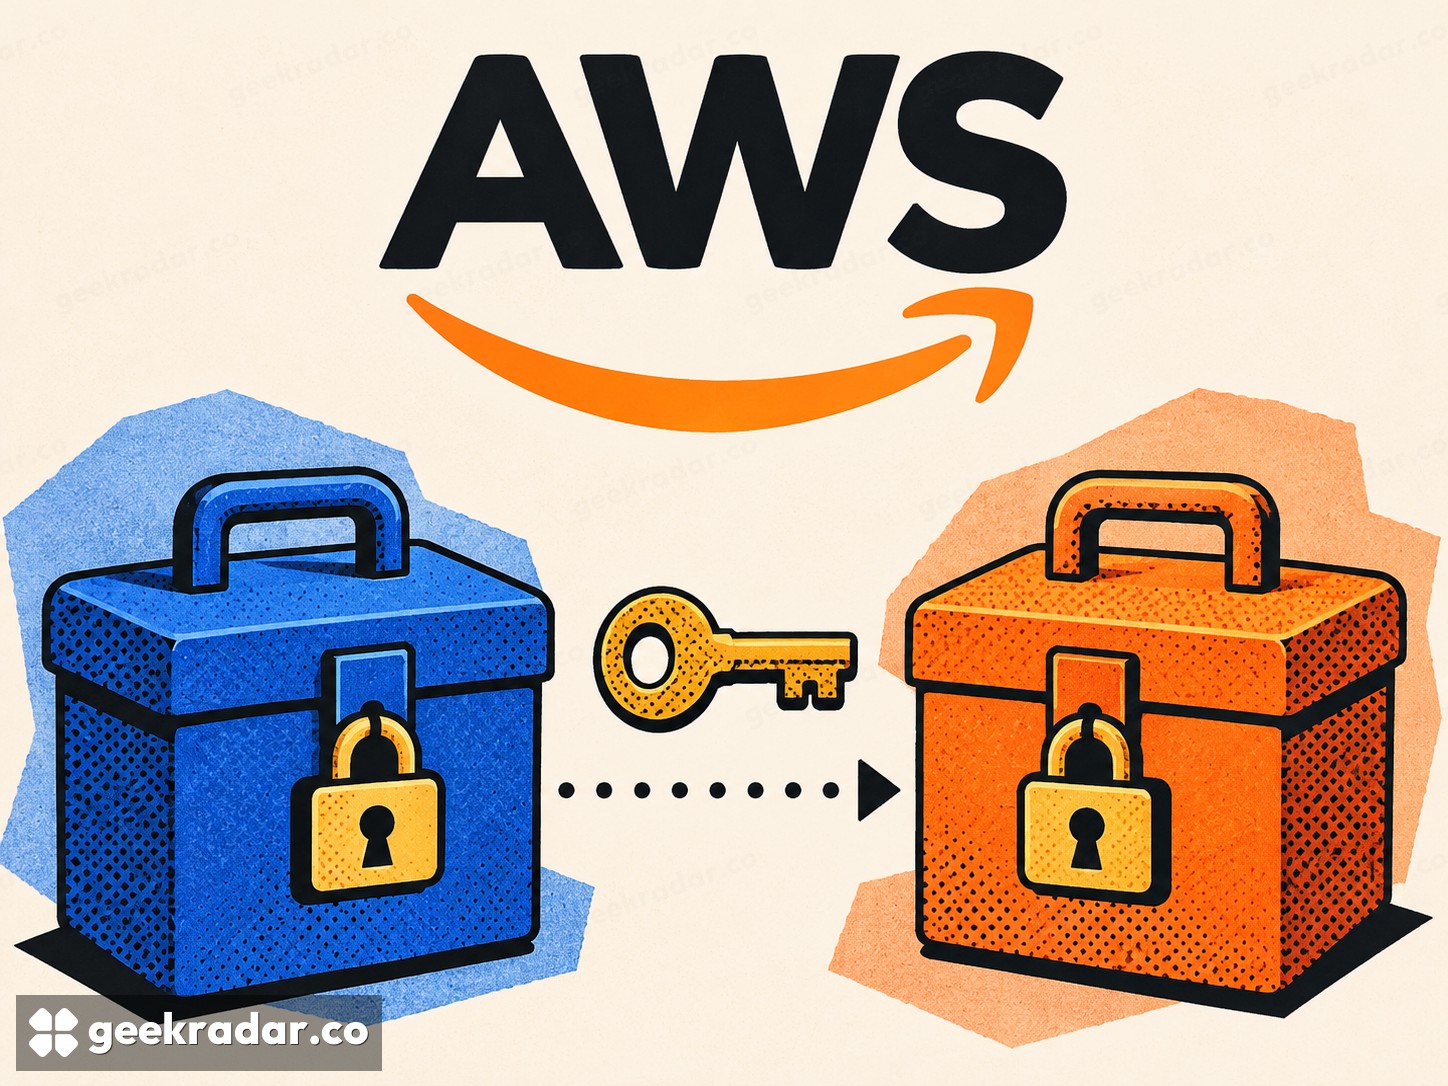
AWS Secrets Manager can now keep a synchronized copy of a secret in a second AWS account, allowing the receiving account to use its own encryption key and access controls. The feature reduces the need to make applications reach across account boundaries every time they need a centrally managed credential. Its most important boundary is easy to overlook: the primary and replica must be in the same AWS Region.
The November 13 announcement positions cross-account replication for shared access, backup and disaster recovery. A replica can be promoted to a standalone secret. That is useful isolation at the account level, but it should not be confused with protection against the loss of the entire region.
One value, separate control
A secret is commonly a credential or another sensitive value an application needs without embedding it in source code. In this arrangement, the primary account can continue managing and rotating the value, while the consuming account holds a local resource encrypted with its own customer-managed AWS Key Management Service key.
AWS’s replication guide describes a two-party setup. The receiving account creates and configures the replica; the primary account associates it with the source. Neither side’s participation should be treated as an invitation to grant broad access to all secrets.
There is currently at most one cross-account replica per primary secret. A design with many consuming accounts therefore cannot assume this feature directly creates an unlimited fan-out tree. That constraint belongs in the architecture discussion before a team replaces its existing distribution process.
Local does not mean instantly current
The replica follows primary value changes, including rotations, through eventual consistency. In practical terms, a rotation can finish on one side before the other side has the new value. Monitoring the replication status is therefore part of deciding whether a failover copy is ready, rather than just checking that a resource with the right name exists.
AWS exposes states including Pending, InProgress, InSync, Failed and Detached. “InSync” is the meaningful healthy state for the copied value; “Detached” indicates that the relationship has stopped. The distinction prevents a subtle operational error: a secret can remain present and readable after it has ceased following future updates.
The broader application also needs a rotation strategy. Copying a new password does not establish that every database connection has refreshed its cached credential or that an old value remains accepted during transition. Those are application and service behaviors beyond the replication feature.
Recovery is more than copying a password
The accounts retain separate tags, resource policies and KMS keys. That separation is useful because the recovery account can have its own access rules. It also means operational metadata cannot be assumed to travel automatically with the secret’s value. An access policy or alerting convention needed in the second account must exist there deliberately.
For a recovery plan, test the whole path: the replica is synchronized, its key is usable, the intended role can read it, and the destination service accepts the credential. A secret copied perfectly is still of little help if the application’s database or network route is unavailable.
Cross-account replication makes one part of that process cleaner by turning the receiving copy into an independently controlled resource. Its value is greatest when the team can name the failure it is isolating. Account separation can help a recovery design; it cannot quietly stand in for regional separation, nor for a rehearsal of the application that must come back online.